Wednesday, May 9, 2018

ICMC18: Update on the Automated Cryptographic Validation Program (ACVP)

Udate on the Automated Cryptographic Validation Program (ACVP) (C12a) Apostol Vassilev, NIST, United States; Tim Anderson, Amazon, United States; Harold Booth, NIST, United States; Shawn Geddis, Apple, United States; Barry Fussell, Cisco, United States; Bradley Moore, NIST, United States; Robert Relyea, Red Hat, United States

[Note: I cam in 25 minutes late and missed the demo]

Previously crypto vendors would lock down their releases against major OS releases, but with ACVP we an do more frequent validations. This just wasn't possible before at all.

Thinking to earlier talks - we need to think about the cost of not doing anything. It should not be compliance vs security (think to the airplane example), this way we can have both.

Given the pace of innovation, we are constantly doing production releases, but it's contrary to the FIPS 140-2 validation. Even if people wait for the validation, they often do not deploy it as described in the security policy, or allow restricted algorithms.

Faster and easier validations means more choices for governments and those that require validated products. That will bring the price down.

Question on anticipated cost - No answer, yet, but it can't be free. We have to be able to pay for hosting services at Amazon, developers and maintenance work on tool. Bigger companies may do a subscription model, smaller ones may want to do one-offs. Want to make it workable and affordable in both models.

The demo server is available now on git hub  - instructions are online on how to get access. Now is the time to come and play and find issues. This is going to be locked down this summer, so sooner rather than later would be good. This will be "shipped' in October.

Right now, only authorized vendors will be able to participate, will need some site visits, etc., to get set up. Processes still being defined.

when will the working group be open to the labs? NIST started out by working directly by talking to vendors, because they had accidentally outsourced that job to the labs. Want to continue to keep the dialogue open to vendors. Labs will have a role, but not necessarily in this working group (possibly via CMUF, etc).. It's  a lot of work and energy to handle what is currently happening, will figure out the right way to engage.

Will the NV lab certification for vendors be the same as the labs do today? If they want to be certified  as a lab - then, yes.  Do you have to do this if you want to keep working with CAVP? Only if you want to use the automated system, or  you can continue to work with a lab.

There will always be a demo environment to try against before you final testing, and even receive test vectors. You can integrate this into your CI (Continuous Integration) framework.  You should be doing this early and often. There is lots of documentation out there. Currently works in MacOS, Windows and Linux environments.

Right now, labs answer our questions - who will do that in the future? That could still be the labs, no reason they could not help you do this.

Good session!


ICMC18: Using FPGAs in the CLoud for Decentralized Trusted Execution

Using FPGAs in the Cloud for Decentralized Trusted Execution (G12a) Ahmed Ferozpuri, George Mason University, United States

Started with an overview of TPM (Trusted Platform Modules), widely available in servers and laptops.

[reminder: these are the notes from the presentation and do not reflect the views or opinions of myself or my employer]

Intel has Software Guard Extensions to create a trusted environment within the chip. It's boundary is at the CPU, data outside the core is encrypted. It helps you avoid snooping and has better application state measurement (attestation), but there are concerns as well.

Data about the code, data, stack, heap is stored in the MRENCLAVE. They can be identified by their EPID processor group ID. Right now, remote attestation requires connecting to Intel's attestation servers.

You can use TEEs (Trusted Execution Environments) for secure cloud and multi-party computing, HSMs (see paper on Barbican integration from Intel Labs), Public Blockchains (PoET, etc).

Resource Efficient Mining (REM) is a goal to reduce energy waste in Bitcoin's Proof of Work. It uses Proof of USEFUL Work instead. This leverages Blockchain agents on the network that you can trust. There is a lot to explore here for new avenues in secure computing technologies.

FPGAs are becoming more common, can use Amazon's HDK to develop your own custom logic. Leverage Physical Unclonable Functions (PUFs).

The slides went by a bit too fast to take accurate notes, lots of proofs (Proof of Secret, Proof of Instantiation, Proof of Execution) and diagrams :-)


ICMC18: SP800-90B Testing Process, Result Bounds and Current Issues

SP800-90B: Testing Process, Result Bounds, and Current Issues (G11c) Joshua Hill, Information Security Scientist, UL, United States

We started out with just hand waving  for evaluating entropy - now, after several iterations, we have NISTs SP800-90B final - YAY! But, I had to submit 20 pages of comments.

Major comments: High-entropy noise sources fail the Restart Sanity Check much more than expected. Entropy and noise sources are required to have the same entropy rate across all process characteristic's and all environmental conditions and required to be stationary!
By more than expected... 60x more frequently than expected! There's a statistical test problem

No noise/entropy source behaves the same way across variations or temperature or voltage changes - nobody could comply!

We need to characterize what are the entropy-relevant parameters and asses appropriately.

We also have issues with noise source definition - output can be the XOR of the output of multiple copies of the same physical noise source. Think of deterministic ring oscillators - fixed period. ... get a nice flat, low entropy. Statistically looks good, but not in reality. (don't do that!)

We've constructed various simulated noise sources and models - the work is a larger scale version of DJ Johnston's 2017 work using NIST's reference python implementation. This testing occurred using only the full set of non-IID tests. First pass - looks much better!

Set up a bunch of other models, including one where you might have bad grounding, etc. (Narrow Gaussian noise source, 8-bit ADC, Sinusoidal Bias), and an idealized ring oscillator.

The models are somewhat complicated, and can return a range of entropy values for each parameter set. The lower end off the modeled range is the value that out to be used in our assessments.

It's vital to test only raw data, and to filter out extraneous signals. Don't perform statistical testing on conditional data!


ICMC18: Keynote: Hardware Security Modules: Past, Present and Future

General Technology Track Keynote: Hardware Security Modules (HSM), Past, Present and Future (G11a) Bruno Couillard, Crypto4A, Canada

Don't be offended if a product you worked on is not mentioned, this is not a complete history, but a start - we want to focus on where we are going!

If you go back in time before the 1970s, encryption was just for government - like weaponries. Not until DES (IBM) did cryptography come into the public space, followed closely by Diffie-Hellmen and RSA. ECC has actually been around since the early 1980s!

When the early 1990s came about, the rest of the world found out about this thing called the Internet. Suddenly we needed to solve problems of commerce leveraging PKI and SSL - we suddenly needed HSMs.  The rate of change has accelerated with things like Cloud Computing, IoT and Blockchain.

The HSMs and FIPS 140-1 all popped up around the same time, a quick succession of product releases like Entrust, Verisign, nCiper, Chrysalis-ITS. RSA 1995 was the year of the HSM - this kick started the industry.

IBM had an HSM that was one of the first to go through the FIPS 140-1 validation.  Then RSA started issuing certificates, but needed a secret keeper - SafeKeeper (rumor has it that it ran off of a car battery).

There were Chrysalis-ITS PCMCIA cards, and others made dongles, but then Smart Cards started coming into fashion (lighter and cheaper).

Around that time, nCipher saw another niche to enter - not just to keep the secrets safe, but to also accelerate. Faster vs higher security.

At one point there were desktop HSMs, they started going for tougher FIPS 140-1 levels.

Then nCipher/Luna/Utamaco/others started moving into the network attached HSM - since 2000, these are getting deployed in large volumes.

Many people working in HSMs were coming from a military background - they were considered weapons, hands on devices.  We need to shift away from that high touch model - we can't expect people to go and hand configure 1000s of devices.

We need to look at the challenges of insider threats, security zoning and patch management. As we move into quantum computing as a reality, we need to think about baking in cryptographic agility now - prepare for over the air updates.  These new algorithms will not likely look like what we have now - they may be bigger, have different attributes, etc.

Can we get to the point where we can have unattended or hostile deployments? How will this work with complex and sensitive application deployments?

Looking forward - we are shifting from a privacy challenge to an integrity challenge. I want to know that the software on my car came from the expected vendor and hasn't been modified. That the software running the elevator hasn't been tampered with.  We must have a trusted supply chain.

We need things to be easier to deploy, think about a home security system - there will not usually be highly qualified IT experts in the home to deploy.

Can we do to the HSM what Apple has done for the cell phone? I think we can!

ICMC18: Plenary Keynote Sessions

Yi Mao, atsec, welcome

This year's conference has more than 400 attendees from 26 countries and 9 tracks! The conference focus is Security First! We started with a very cute video.

Plenary Keynote Address: Digital Disruption and the Implications for Cybersecurity and Cryptography (P10a) Jason Hart, CTO Data Protection, Gemalto, United Kingdom

It took radio 38 years to reach an audience of 50 million people. Television only took 13 years to reach an audience of 50 million.

It only took 4 years for the world wide web to reach 50 million. We all started with modems, remember Hayes modems? US Robotics overtook them with their easier to use modems

Facebook took only 2 years to reach 50 million subscribers. 1 in 7 divorces are blamed on Facebook - a new sales chanel for divorce attorneys!

Pokeman GO - took 19 days to reach 50 million users. 19 days!

Nobody goes to the library to search for information anymore, even search websites are getting pushed out by higher order services like Alexa.

Digital Disruption - 10x innovation, 1/10th the cost and 100x the power.

In this time, you need to look for problems to solve. For example, look at Tipsy Robot - a drink making robot, that makes the experience for users easier and simpler (and consistent and eliminates standing in long lines).

Is our industry easier and simpler to use?

Amazon Web Services (S3) was easier to use than others - completely disrupted the market.

Look at some market leaders - uber, facebook, Alibaba and AirBNB - they don't have inventory, cars, or create content. They are changing the market by being simple, filling a need and they are habit forming.

What are we doing to make cryptography easy? There is an opportunity here.

Data is being created at an astronomical rate - 90% of the data was created in the last 2 years.

All businesses have secrets, it is our job to help them keep their secrets safe.

Out of all of the breaches last year, he believes only 1% had the proper cryptographic controls in place. Why? Everyone knows the importance of using cryptography - but it's too hard to use. We have a huge opportunity as a community here - everything needs what we're doing.

Traditional approaches have to change. What does the user need? Will we evolve or not?

We have the tools to solve the problems for trust and data privacy. We need to reset our expectations of users that use our security solutions.  We need to make it exciting and fresh. Adoption will happen.

User is worried about data integrity - they don't connect it to what we do. We need to be working at that level and worry about the implementation details ourselves.

IoT will be driving cryptography adoption in 2018 - we need to be ready as an industry to provide the right algorithms and options the industry needs.

We are moving away from Platforms as a Service, etc - and moving into functions as a service.

We know quantum is coming - are we crypto agile? Are we enabling our customers to be crypto agile?

The future will be decentralized - can we meet that need?  Can we do it simply?


Plenary Keynote Address: What’s Next for Cryptography? How CSE Balances Privacy and Innovation in the Public and Private Sectors (P10b) Scott Jones, Assistant Deputy Minister, Information Technology Security, Communications Security Establishment, Canada

CSE is Canada's cryptography leader, and need to protect the most important information, watch for threats and stay ahead of the industry.

CSE had in recent times been very focused on cyber threats and lost their focus on cryptography, which is the backbone of security. There will be a renewed focus on cryptography.

Cryptography is more widely deployed than the average user is aware - and that's okay, it should just work.

There are proposed changes to authorities and capabilities for CSE, including increased accountability measures.

People say that privacy is dead, but he believes that cryptography needs to play here to give people the option of privacy. In fact, it's our only option to maintain our privacy.

Breaches will happen - you can't protect against them all, so you need cryptography.

Unfortunately there is a lot of misinformation out there - that little lock on your browser is marketed as 'protecting your data' - true for in transit, but what happens on the other end?

Good cryptography implemented poorly is worse than none- it creates a false sense of security.

CSE will become (again) a proactive agent for research and standards, validation programs, secure tailored solutions program and cloud computing.

Government can't match the pace of innovation and speed of delivery of what is happening in industry, need to leverage that work for all except the most specific needs. Need to partner with industry here - share our knowledge and learnings.

Sitting in a building and being locked to a desk is no longer a method of securing data.

We need a variety of validated commercial products to choose from to meet different needs. We need to keep pace with new security vulnerabilities in commercial products. We need to evolve quickly.

Take the aircraft industry - they have to use only validated modules. But a security vulnerability has come out and is patched, but if they patch ... invalidates their validation.  We should not be making the industry make these choices.

Our technology is too hard to use - too many breaches are related to misconfigurations. If a misconfiguration allows a cloud deployment to be breached, we need the data to be securely encrypted.

We must avoid the arrogance problem - we don't have all the answers. We need to work together to solve the tough problems. We need to make our technology accessible - people don't even know what to ask for.

We want to start publishing our research questions - get your input and hopefully you can share your problems as well, and hopefully create partnerships to solve them.  Looking to partner both inside and outside of the government - we all have pieces of the solution. we can't solve these big problems without industry.

We are creating the Canadian Center of Cybersecurity - the Cybercenter will bring together many different research fields, and cryptography and cryptology will remain at the central focus, it ties everything together.

This conference will strengthen the world's Internet, it will strengthen commerce, it will make the world a better place.

We should not be content with the status quo or ever believe we've solved all of the problems.

Creating a quarterly cyber journal to try to bring security topics to the general masses, looking for submissions for cryptography.

Consumers are looking for features, we're looking 10-20 years ahead on how to keep the Internet secure.


Monday, January 8, 2018

2017: Year in Review

What a year! I can't even begin to remember everything that happened, but here are some highlights and lowlights.

Highlights 
  • After 20 years, I left Sun/Oracle and joined Intel as a Director of Software Engineering of Security Solutions Enablement for Data Center.  A long title that means my team works on security related projects, like Open Security Controller, that enable security on the Data Center. 
    • I worked at Intel 21 years before, as an intern in their Folsom Engineering Services group (as an admin for Win 3.1, WinNT, Win95, AIX, Irix, SunOS and Solaris).  It was oddly like like putting on a comfortable pair of shoes coming back, but at the same time a very different company. A much faster moving place, a more inclusive place and more inventive place.
    • My team has released two versions of Open Security Controller (0.6 and 0.8) this year! (like I said, fast moving!)
  • I was appointed to the City of Mountain View's Bicycle/Pedestrian Advisory Committee, where I get to advise the City Council on such things like: transit projects, walk-ability of new building projects, how to improve dangerous and deadly intersections, and where to spend budget to improve biking and walking.  It's pretty fun! The committee definitely has diverse opinions and I have found the last twelve months on the committee to be quite a learning experience.
  • I demonstrated, with my Oracle team, PKCS#11 and KMIP on Solaris at the RSA Conference Expo in San Francisco in February 2017.
  • I read 24 books, covering 7,937 pages.
  • I recorded the narration for 8 audio books for Learning Ally. These books are for the blind and others with reading disabilities.
  • I did a police ride-a-long with the Mountain View Police Department! I was amazed at the officers compassion, how well they treated the citizens and how they were quick to de-escalate a situation.  I watched an officer arrest a man who had been drinking "since the early morning" and then brandished a knife at another man at Walmart. The man was belligerent when first approached, yelling and gesticulating.  The officer used calm tones, did a quick and calm search, secured the gentleman and proceeded with his investigation. I watched a situation go from tense to calm in a heartbeat. Yes, I used the word calm repeatedly - but that is the best way to describe what the officer did.
  • I was on the Crypto Review Board for BlackHat USA, and got to attend!!
  • Additionally, I was on the program review boards for International Cryptographic Module Conference (ICMC) and GreHack!
  • I presented on PKCS#11 version 3.0 at ICMC.
  • I became secretary of the PKCS#11 technical committee, a role change from co-chair.
  • I reviewed scholarship applications for Learning Ally Scholars - every one of the students was incredible!
  • My husband and I celebrated 10 years of marriage in Sausalito, CA.
  • I saw all of my siblings and my parents this year! Most more than once! I didn't see enough of my nieces and nephews, though...  
  • I did a few more Murder Mysteries, did photography for a couple of shows, and sang with the Lyric Victorian Carolers.
  • Overall, I volunteered more than 179 hours.
  • I went skiing!
  • I stayed alive!
Lowlights
  • I lost my uncle, Dan Bubb, my Dad's brother, to pneumonia.
  • My dear friend Elisa was diagnosed with breast cancer in October and Comcast let her husband go from his job (along with the rest of his division) in December - just before Christmas.  Her battle continues, please consider donating.
  • I suffered a major health crisis myself - on my first day of work at Intel, where I learned another highlight: Intel is a compassionate company, they were there when I needed them and helped me to get back on my feet and hit the ground running in my new role!  And, I didn't die :)
Any lowlights or highlights for you?

Here's to 2018!

Saturday, December 16, 2017

Please Support Elisa's Battle Against Breast Cancer

Hi Folks - One of my best friends from the 3rd grade on had just moved into a new home in October with her family only to discover she had a very fast growing breast cancer. She discovered it via self exam and it tripled in size over a couple of weeks while she was prepping for chemotherapy.

To make matters worse, her husband (and his entire division) was let go from his job this week.

Elisa has been a stay at home mom for her special needs children for the last several years, so the family has lost their only income source while she is very sick with chemo treatments. Losing a job unexpectedly is never easy, but losing it 2 weeks before Christmas while your wife is trying to stay alive is absolutely devastating.

In addition to having cancer, Elisa has a degenerative genetic disorder (Ehlers-Danlos Syndrome) that already was causing many problems for her body. If you can give anything, please do. God bless.

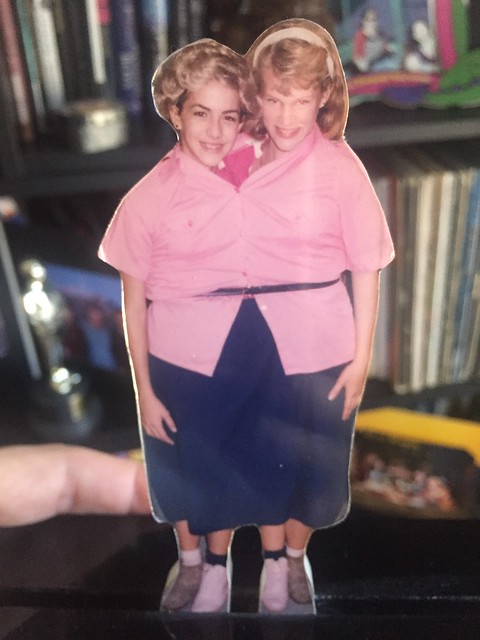
Elisa and I in 6th grade.

When we both lived in Fort Wayne, IN, we were literally inseparable.  In the 6th grade we convinced our teachers that we could go to the other's classes (instead of our own) so we could wear this Halloween costume).

As to why it's Defeating Voldemort? Her children decided that was the tumor's name and because they love Harry Potter, they just know he can be defeated.

Her GoFundMe link can be found here.  Thank you, thank you, thank you.

Valerie